Executive Summary
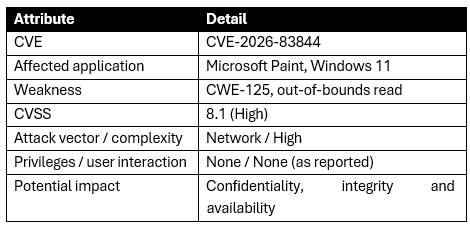
CVE-2026-83844 is an out-of-bounds read (CWE-125) in Microsoft Paint on Windows 11, scored CVSS 8.1. The weakness itself is ordinary, what makes it relevant to us is where the fix lives. Paint is serviced through the Microsoft Store, outside the Windows cumulative update channel, so an endpoint that passes every OS-level compliance check can still be running a vulnerable Paint package.
The picture is further complicated by changing fix guidance. Between 13 October and 5 November, the stated minimum patched version moved from 11.2605.91.0 to 11.2609.401.0, and some endpoints with automatic updates enabled were still reported on older builds. Until this settles, we advise treating Paint as a separate patch item in your vulnerability management process and verifying package versions directly, rather than inferring status from the Windows build.
Why This Matters to Your Organisation
Most compliance reporting built on Windows Update, WSUS or Intune tracks the operating system build. Store-delivered applications such as Paint sit outside that view. A workstation can be reported as fully patched while carrying an older application package, and that gap is invisible to dashboards that only read the OS build.
This matters most in environments where the following are true:
- Windows 11 endpoints are widespread, including administrative workstations, branch machines and kiosks where Paint is installed by default.
- Store updates are restricted, delayed or managed separately from OS patching.
- Vulnerability reporting is presented to auditors or regulators as evidence of patch posture.
For financial institutions, fintechs and government bodies, an incomplete baseline means that evidence overstates actual coverage.The unstable fixed-version guidance adds a second problem. If the target build is not agreed, teams cannot define what “compliant” means, and remediation cannot be measured or closed out.
Technical Summary
Recommendations
- Audit Microsoft Paint versions across Windows 11 endpoints.
- Validate installed versions against Microsoft's latest fixed-build guidance.
- Prioritise outdated installations for updates or temporary removal where necessary.
- Review image-file associations and restrict untrusted files to approved applications.
- Include Microsoft Store applications in routine vulnerability assessments and patch compliance monitoring.