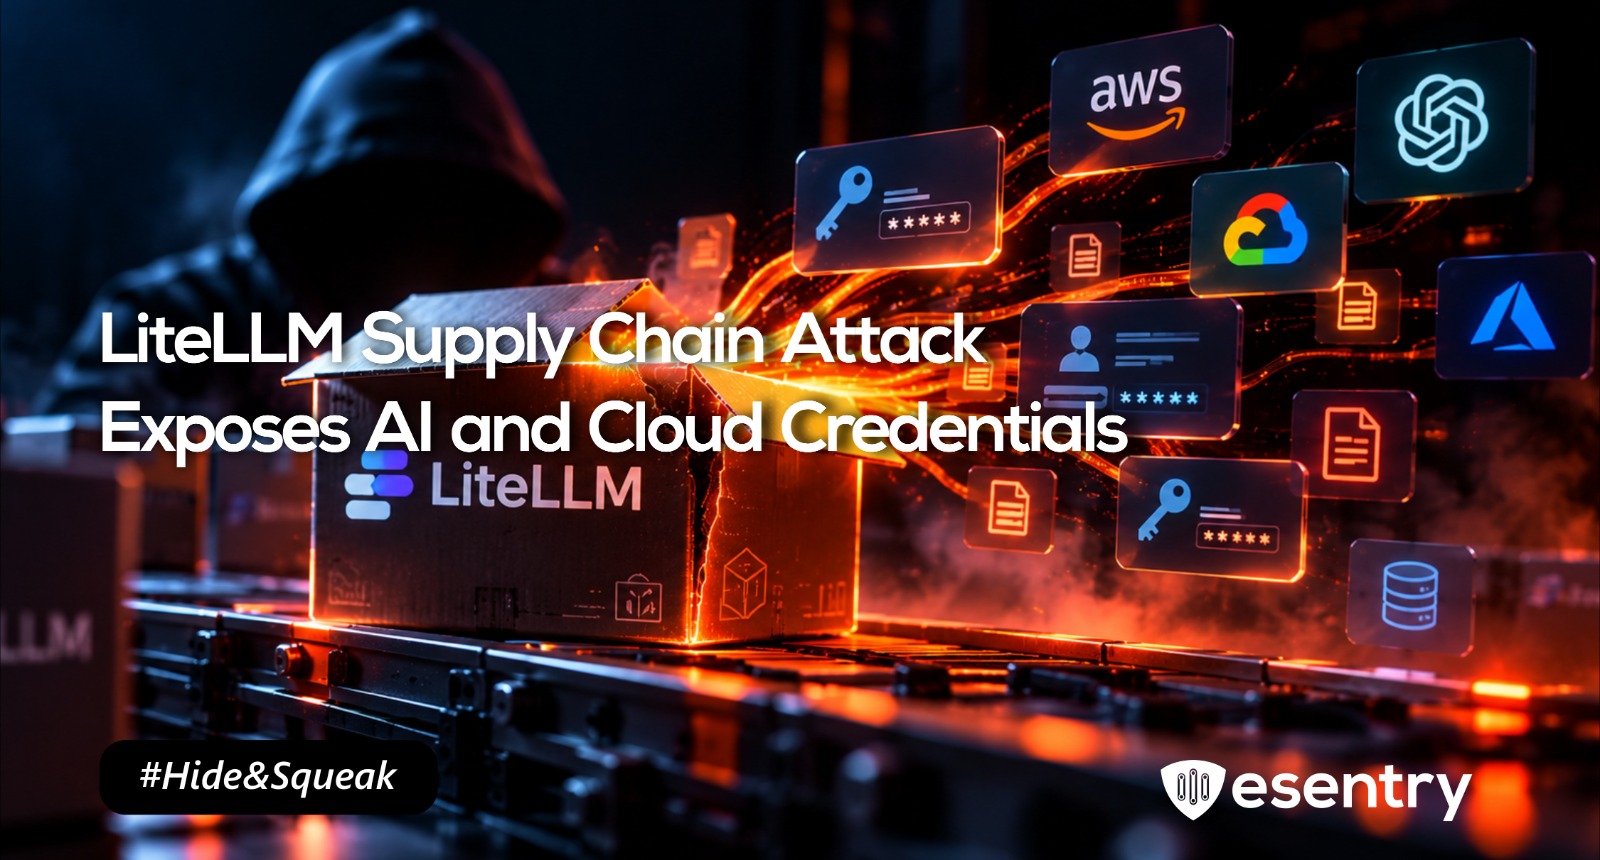
A software supply chain attack compromised LiteLLM, an open-source Python library used to connect applications to multiple AI models. Attackers distributed a malicious release containing credential-stealing malware and a backdoor through PyPI and container registries.
The compromised version, LiteLLM 1.107.0, was designed to steal cloud credentials, AI service API keys, developer secrets and browser data. The malware could also download and execute additional code.
This incident highlights growing AI security risks and software supply chain threats affecting organisations that rely on cloud services and AI applications.
Potential Impact
The attack could expose:
- Cloud credentials: AWS, Google Cloud, Azure and Kubernetes secrets.
- AI service API keys: Credentials used to access AI models and services.
- Developer secrets: SSH keys, Git credentials and package registry tokens.
- Sensitive information: Browser data, application secrets and environment variables.
Successful exploitation could lead to credential theft, account takeover, unauthorised cloud access and data breaches.
Affected Versions
- PyPI: LiteLLM 1.107.0
- Docker Hub and GHCR: Affected tags include v1.107.0, latest, main-latest and main-stable.
Datadog identified version 1.106.2 as the latest safe release at the time of its report. Verify release guidance before redeployment.
Recommended Mitigation
- Identify affected Python environments and container images.
- Remove compromised packages and inspect for malicious startup files, including cook.pth, cook.py and sitecustomize.py.
- Deploy a verified, unaffected LiteLLM release.
- Revoke and rotate potentially exposed cloud credentials, AI API keys, developer tokens and SSH keys from a clean environment.
- Review cloud audit logs, authentication records and release pipeline activity for suspicious behaviour.
- Strengthen software supply chain security through least-privilege access, protected release workflows and package integrity verification.
The LiteLLM supply chain attack demonstrates how compromised developer credentials can introduce malware into trusted software releases. Organisations should investigate potentially affected systems, rotate exposed credentials and strengthen monitoring to reduce the risk of further compromise.